Security and governance software for growing teams.
Protects brings risks, policies, employee training, assets and evidence into one workspace. Use it with your own team, or combine it with agreed YDC advisory and hands-on support for ISO 27001 and customer assurance.
See how Protects works
Explore the workspace with example data. The interactive Storylane demo loads when you open it.
View the interactive product tour
Hoping for the Best is not a Strategy
Scattered policies, unclear risk ownership and missing evidence make security harder to manage. Protects helps your team keep the work organised and ready to explain when a client, insurer or assessor asks.
Risks nobody has a clear view of
Policies that live in inboxes
Supplier checks lost in email threads
Training nobody can evidence
Actions tracked in spreadsheets
Tools that never quite join up
Keep everyday security work connected.
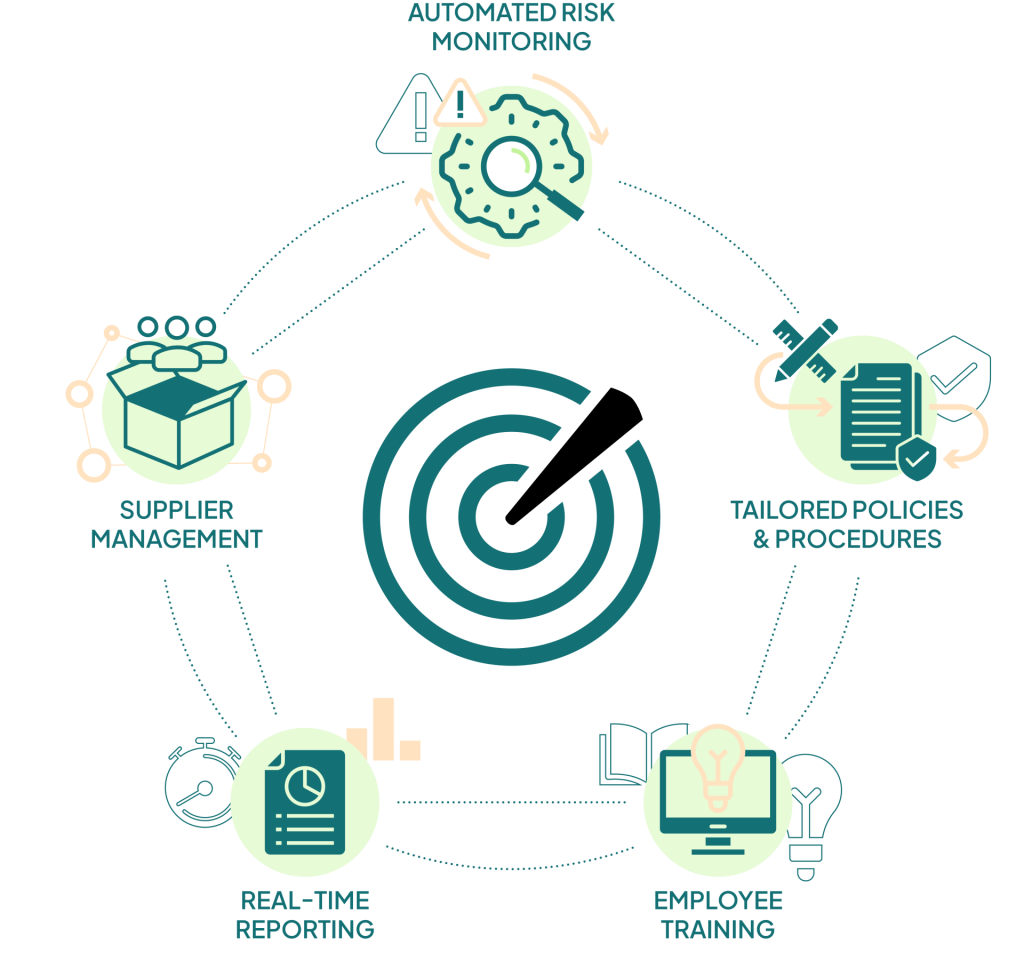
Bring risks, policies, employee training, suppliers, assets and evidence into one workspace. Keep responsibilities clear and records connected as your team works.
Used day to day by growing organisations

GLXG Expert Labs
End-user training and risk management - reducing people risk and building a secure foundation.
Tax Desk
TaxDesk maintains ISO 27001 with YDC and Protects, reporting 80% lower costs and audit preparation reduced from months to days. Ongoing senior support helps maintain its ISMS. These are client-reported results for this engagement, not guaranteed outcomes.
Nekta Drinks
Compliance built on culture - supporting a growing social brand without slowing it down.
Desucla
Desucla achieved Cyber Essentials, Cyber Essentials Plus and ISO 27001 with YDC. Ongoing senior GRC and information security support includes an agreed competent individual to help maintain the programme.
Built for regulated, risk-aware organisations.
Different sectors. Different pressures. Same control.
Legal
Show clients and regulators that data protection and control are built into how the firm operates.
Accounting
Give clients confidence that training, controls and supplier checks protect their financial data as standard.
Health
Protect patient and client data with clear ownership, live policies and supplier checks that stand up to scrutiny.
Digital / MSP
Turn security and risk management into a visible value-add for clients, not an awkward cost centre.
SME
Run the business with the same discipline as a larger organisation - without slowing things down.
Built by people who’ve lived these problems.
Protects reflects how security actually gets tested in the real world. Not in theory, but when auditors, clients or regulators ask questions and expect clear answers.
It’s built for teams who are doing the right things, but struggle to show it without last-minute effort. Protects makes that work visible, repeatable and easy to stand behind.
Paul Reynolds
Co-founder of Protects
CISSP · ISO 27001 Lead Implementer
Choose the software and support your team needs.
Start with your use case, then agree the level of help you need. Standard is software-only; Assurance adds agreed YDC advisory support; Managed adds agreed hands-on practitioner delivery. Each option is scoped and quoted around your organisation.
Standard
Software-only
Protects gives your team a workspace to manage the agreed policies, risks, training and evidence. Your team operates the programme.
Assurance
Agreed advisory support
Protects with agreed YDC advice to help your team interpret requirements, review progress and keep the programme on track.
Managed
Agreed practitioner delivery
Protects with agreed hands-on YDC support for the governance and security work in your proposal, alongside your leadership and IT provider.
Three practical starting points
- Employee training: organise security awareness, assignments and completion evidence. Agree the people, content and support included.
- ISMS provision: bring ISO 27001 policies, risks, responsibilities and evidence together. Agree software access separately from implementation, ongoing reviews and independent certification-body fees.
- Risk assessment: scope an ISO 27001 information security risk assessment or a general IT risk assessment, with agreed workshops, deliverables and follow-up support.
Each use case is separately scoped and quoted. Supplier management and third-party risk management (TPRM) packaging and pricing will follow. Contact us to discuss your requirements.
Your proposal confirms enabled features and integrations, access and allowances, onboarding, support time, review frequency, fees, VAT, billing and minimum term. Preparation, technical remediation, third-party certification audits and additional work are excluded unless expressly included. Your organisation remains responsible for operating controls and approving decisions.
Can we use Protects without YDC consultancy?
Yes. Standard is software-only for your own team to run. Assurance and Managed add the YDC advice or practitioner work agreed in your proposal.
Does Protects guarantee certification or compliance?
No. Protects helps organise the work and evidence. Your organisation must operate its controls and meet the applicable requirements. An independent certification body decides ISO 27001 certification. See how YDC supports ISO 27001.
Find the right starting point.
Tell us whether you need employee training, an information security management system or a risk assessment. We will help you choose the software and support that fit. We reply to genuine enquiries within one working day, usually sooner. You can keep the conversation by email if you prefer.